
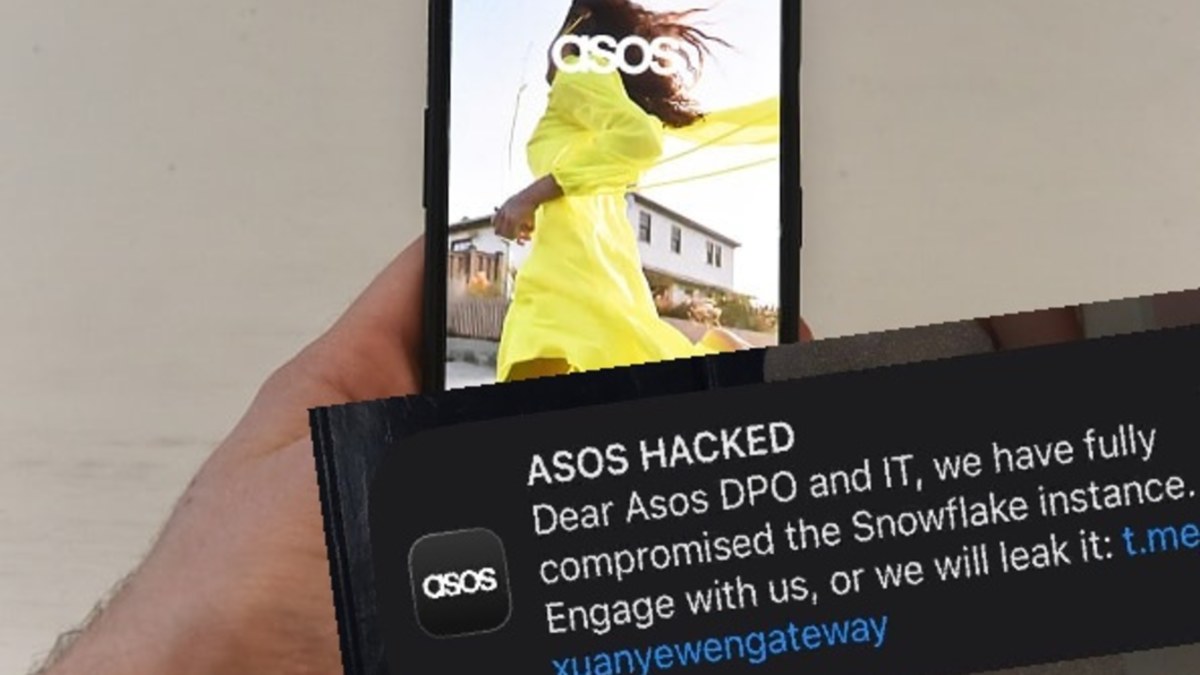
ASOS customers in Australia, UK and other parts of the world have been sharing screenshots of an app notification from the fast fashion brand.
The message sent on Tuesday claims the company’s system has been breached, with hackers threatening to leak customer data.
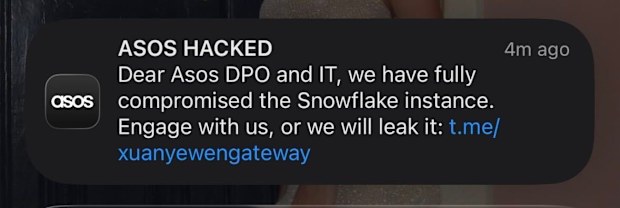
ASOS customers in Australia, UK and other parts of the world have been sharing screenshots of an app notification from the fast fashion brand. Supplied/Mikala Theocharous
“ASOS hacked,” the alert, which was sent about 8pm AEST, reads.
“Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.”
ASOS has not made any announcements to customers as yet about the message and did not immediately respond to nine.com.au’s request for comment.
It’s understood it is still investigating if a data breach has, in fact, taken place.
The ASOS chatbot has said the company is “aware of the notification and are currently investigating” but also noted the app alert “may be a scam”.
“We don’t have any further information to share at this stage, but we’ll provide an update as soon as we know more,” it added.
The link sent to customers via the app message takes people to a newly created channel on messaging app Telegram, labelled Xuanye group gateway.
Cybersecurity experts Sophos told British media its specialists hadn’t heard of this group before and it had not come up on any of the channels being monitored by the company.
ASOS has not made any announcements to customers as yet about the message and did not immediately respond to nine.com.au’s request for comment. Getty
The website appears to still be working as usual with no pop-ups or other messages.
Charlotte Wilson, head of enterprise at cybersecurity firm Check Point, said if confirmed it would be a very serious breach.
“If confirmed, this is a deeply serious attack because the hackers appear to have done something particularly brazen: turned ASOS’s own app into their ransom note,” Wilson told BBC.
“Millions of people trust notifications from apps on their phones because they are supposed to come directly from the company.”
According to Sky UK, the fashion brand, which is based in the UK, employs about 2800 staff and is worth about £602 million ($1.15 billion).
The global retailer has 16.4 million active customers who have shopped in the last 12 months.
The company’s share price had been on the up before the apparent hack but dived by almost 12 per cent on the London Stock Exchange after news of the suspected hack emerged, according to Guardian UK.
What’s a Snowflake?
The message claimed the hackers had “fully compromised the Snowflake instance”, which is believed to refer to cloud data storage company Snowflake.
The company is used by a number of retailers to store sensitive customer information and has been the subject of previous data breaches, including Ticketmaster, Live Nation, Santander Bank and AT&T.
Cybersecurity expert Dan Bird, from Horizon3, said the message to customers suggested the breach had gone beyond the Snowflake database.
The ASOS website appears to still be working as usual with no pop-ups or other messages. Nine
“Sending a push notification to ASOS’s app users would require access to the company’s notification system, which is separate from the Snowflake data platform the attackers claim to have compromised,” Bird told BBC.
“If both claims hold up, it suggests the attackers got hold of credentials that opened more than one door.”
Dray Agha, senior manager of security operations at online security firm Huntress, echoed those sentiments.
“The push notification suggests attackers have breached the systems controlling the ASOS mobile app also. This is clear public extortion,” he told The Guardian.
“Sending a ransom demand directly to consumer devices is an aggressive extortion tactic designed to force the business into a quick negotiation. I strongly advise shoppers to watch out for targeted phishing attempts while we wait for official confirmation of a data breach.”
Customers are being advised to be cautious around follow up emails and messages. Instagram
Under UK law, companies are required to report any personal data breaches to the Information Commissioner’s Office within 72 hours after discovering a breach.
In some instances, they will also be required to report to the National Cyber Security Centre and police.
What should customers do?
Customers are being advised to be on their guard for suspicious activity and follow-up messages.
“High-profile cyber incidents create ideal conditions for phishing attacks,” NordVPN chief technology officer Marijus Briedis said.
“Criminals may exploit the publicity by sending emails and texts claiming to be from ASOS, perhaps asking customers to reset a password, confirm payment details, check an order or claim a refund.”