Artificial intelligence is already changing the cybersecurity equation for New Zealand organisations.
Quantum computing may soon add a more fundamental challenge – the cryptography protecting sensitive data, systems and transactions today could be broken in the next few years.
These powerful technologies are the ultimate double-edged swords. They’ll unlock scientific discoveries, boost productivity, and unlock human creativity. But they are already creating headaches for security chiefs and IT teams trying to keep their organisations’ data and systems safe.
When it comes to AI, cyberthreats are similar to what they’ve always been.
Frontier AI doesn’t invent magic entry points; it hunts for basic mistakes – so, while good cyber hygiene doesn’t stop every threat, it does take away easy targets and forces an automated adversary to work exponentially harder.
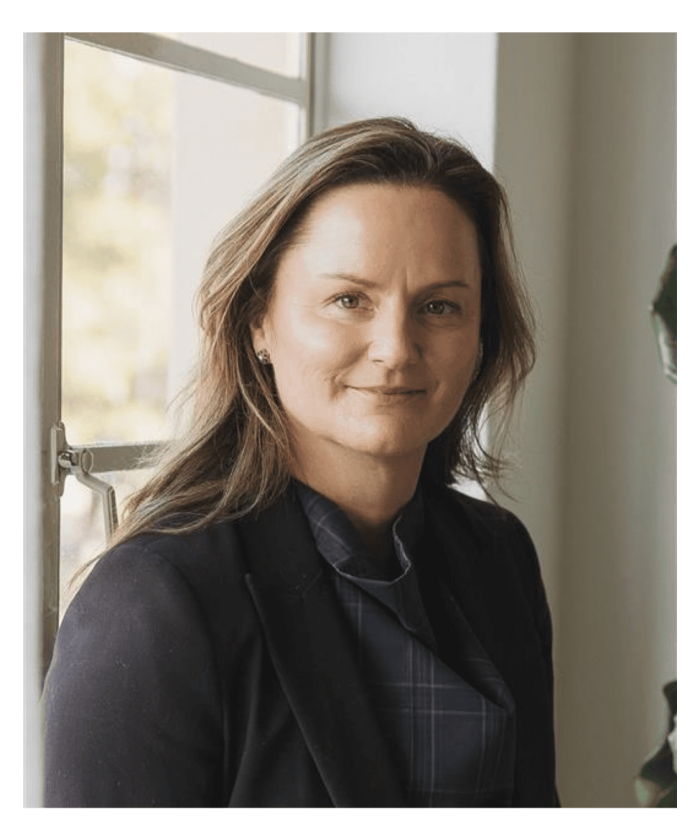 Nicole Henry, Head of GR ANZ, Fortinet
“The pathways and the entry points into everybody’s systems are boringly predictable,” says Nicole Henry, Fortinet’s Canberra-based head of government affairs for Australia and New Zealand.
“It’s still your identity, your access, misconfigurations, password hygiene, and not patching systems. My goodness, if people could simply patch their systems, that would be half the battle won!”
AI enables much faster and more sophisticated attacks. Hackers are using AI to scan networks and websites for security weaknesses, write malicious malware, and launch social engineering campaigns to try and steal your credentials and identity.
A newer risk is “shadow AI” – where your precious data is leaked via inappropriate use of AI assistants and agents, often as a result of employees using unapproved tools for their work.
If you don’t know what data your employees are feeding into unapproved assistants, or what decision-making authority you’ve given your own agents, you’re opening the door to data leaks while having no idea where your legal liability actually sits when things go wrong.
Current encryption may be dead by 2030
A quantum computer will not bring your operations to a halt next week. But the window to prepare for that potential outcome is open, with Australia, the United States, and the European Union requiring organisations to implement post-quantum cryptography (PQC) systems by 2030, at least for critical infrastructure and high-impact systems.
New Zealand’s Information Security Manual, which lays out the government’s expectations for cybersecurity standards, has the same requirement, without mentioning a specific transition timeline.
It means that organisations are confronting three overlapping technology horizons at once, says Henry.
They must continue to manage a complex, often ageing estate of IT and operational technology, adopt and secure AI tools that are being introduced rapidly across the business, and begin the longer-term migration to post-quantum security.
“The challenge is compounded by executives who may not yet fully understand today’s cyber risk, let alone the investment and planning required for the next transition,” Henry says.
Hackers are taking a “harvest now, decrypt later” approach, knowing that the timeframe in which quantum computers will become available is shrinking.
It means that data with a long useful life – intellectual property, health information, customer records, government material and commercially sensitive documents – could be stolen now and held until it can be decrypted months or years down the track.
The migration away from vulnerable cryptographic systems will be complex, particularly for businesses with legacy applications, connected devices, long-lived equipment, cloud dependencies and intricate supplier relationships.
Visibility, governance and practice
Henry’s first recommendation to executive teams and boards is straightforward: understand the digital estate.
“Number one is visibility, across your entire digital technology stack,” she says.
That means mapping systems, data, connections, cryptographic dependencies, identities, third-party suppliers and access rights. It is essential for managing AI today and will reveal the scope of the work required for the quantum transition.
From there, organisations should build a funded roadmap: identify the technologies that need replacing or upgrading, make PQC support a requirement in new procurement, engage suppliers, develop workforce capability, and plan for a hybrid environment in which legacy and post-quantum systems coexist.
But technology alone is insufficient.
Cybersecurity needs board-level ownership, sound governance and regular testing. Henry argues that organisations should operate on an “assume compromise” basis, with clear and rehearsed decisions for maintaining continuity when an incident occurs.
“We can’t start thinking about an attack when it actually occurs,” she says. “We have to have nailed those processes well ahead of time.”
Tabletop exercises – and, where appropriate, practical recovery testing – create the institutional muscle memory needed when an incident unfolds at machine speed rather than over days.
Make cybersecurity a strategic priority
AI also introduces governance challenges inside the enterprise. As businesses experiment with generative AI and AI agents, sensitive data may move between internal systems, cloud applications and third-party environments in ways that decision-makers do not fully understand.
The concern is no longer just an employee pasting information into a chatbot. AI agents can be given access to data and authority to make decisions or take actions across systems. That creates new questions around identity, permissions, data retention, accountability and incident response.
“AI is horizontal,” Henry says. “We have executives who say, ‘Let’s just have a go and see what it can do for us’ without fully determining what the value proposition is that they want to use AI for.”
Her advice to business leaders is to treat cybersecurity as a core strategic priority, rather than a side issue.
For New Zealand businesses, the emerging AI and quantum era is not a reason for panic. It is a reason to begin the work now: map the environment, strengthen basic cyber hygiene, make quantum-ready procurement decisions, govern AI deliberately and practise the response before the pressure arrives.