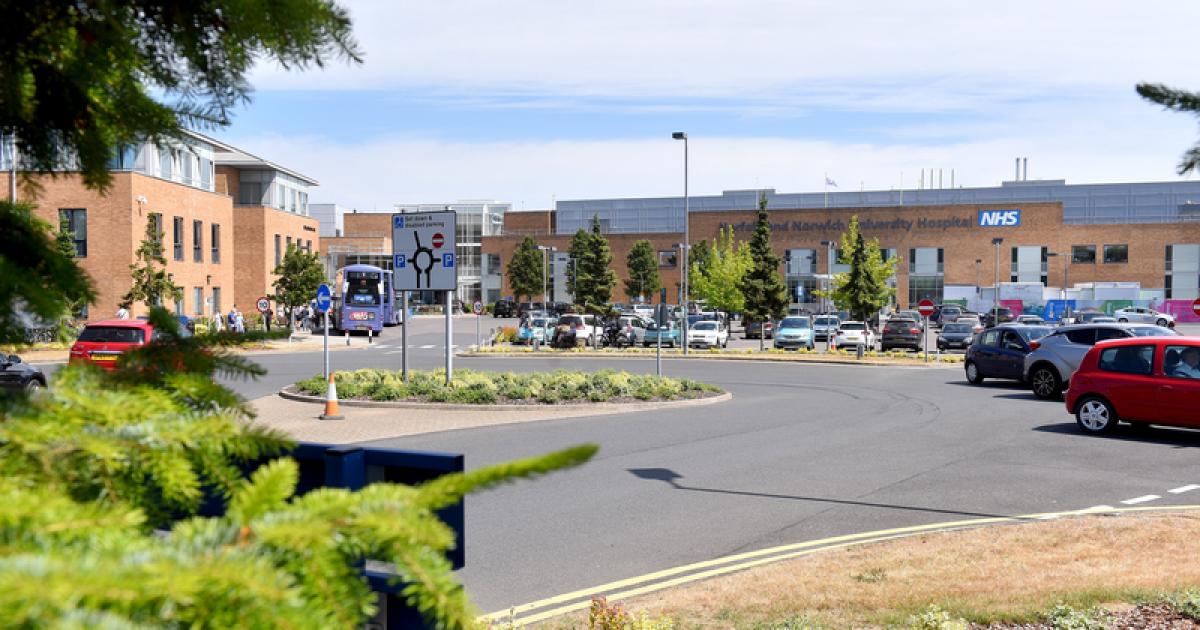
The Norfolk and Norwich University Hospital (NNUH) is currently working to identify individuals whose data was breached in the attack by cyber-criminal group Qilin.
It is believed tens of thousands of patients’ information were swiped in the hack on Synnovis – a third-party testing provider used by the NHS.
Synnovis tests blood, tissue and other samples, and performs laboratory diagnostics for hospitals and GPs.
Crime group Qilin uploaded the stolen data onto the darknet, an area of the internet often used by criminals.
Chris Cobb, NNUH acting executive managing director, said: “We have been notified by Synnovis that data linked to our Trust was included in the material accessed following the cyber-attack which occurred mid-2024.
Chris Cobb, NNUH chief operating officer (Image: NUHH)
“We are working to identify any individuals affected and are adhering to NHS England and Information Commissioner’s Office guidelines.”
Hospital Trusts in Essex, Bedfordshire and London were also affected by the hack.
Qilin claims it targeted Synnovis as a way to punish the UK for not helping enough in an unspecified war.
But the firm said the data was stolen “in haste and in a random manner” from its hard drives in an attempt to extort money.
Action Fraud, the UK’s national reporting centre for fraud and cybercrime, has advised people to contact the organisation if someone claims to have their data.
Data breaches at Norfolk companies
There was another data breach at a Norwich-based company, KLM UK Engineering, in April when hackers gained remote access to a HR drive storing employees’ information and records.
An email sent from the firm’s managing director Wayne Easlea said the drive included personal and contact details, identification and national insurance numbers, car registrations, absence and health records, and bank details.
It is not known how many people were affected by the hack, but the company said it took “appropriate immediate containment actions”.
Earlier this month, Norfolk Constabulary apologised after a data breach involving officers’ payroll information in which a file was mistakenly sent to a former officer.
The force says it was the result of human error and that the recipient had deleted the data.
There is no evidence that the information has been further shared or misused and the Information Commissioner’s Office was satisfied with the response and requires no further action.
“We are sorry for the concern this may cause and are providing support to those affected, ” said a spokesman for Norfolk Constabulary.