How the PHP cyber-security saga unfoldedpublished at 08:43 BST
08:43 BST
 Joe Tidy
Cyber correspondent
 Image source, Getty Images
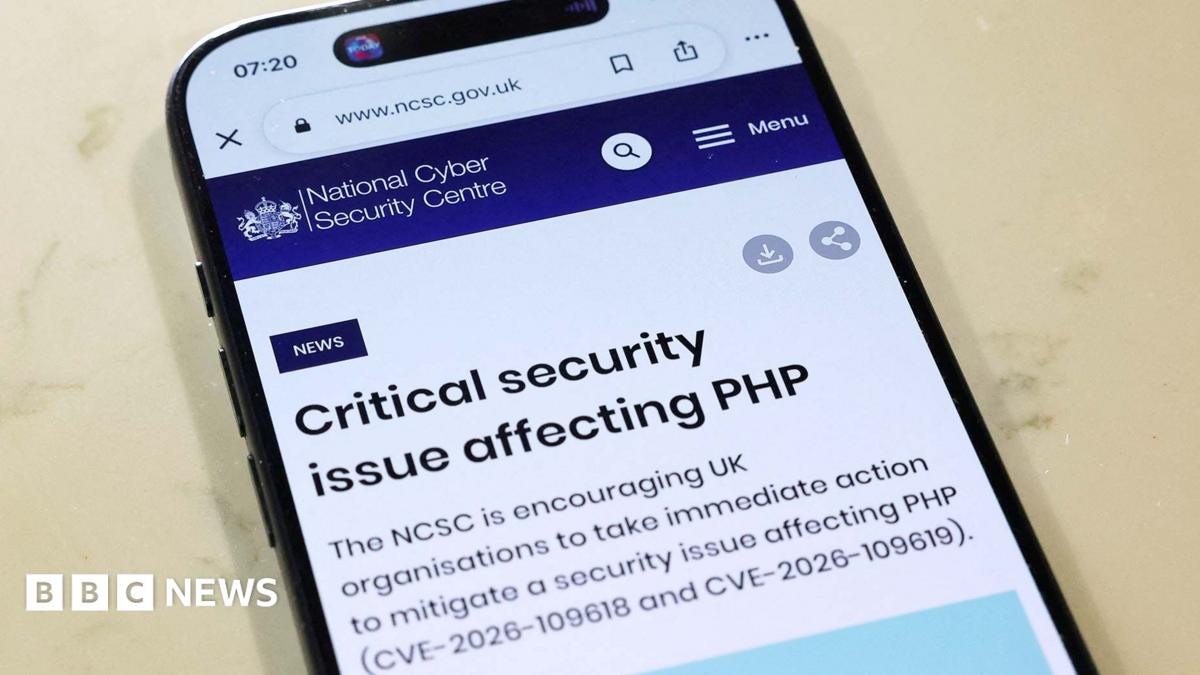
In 2024, researchers at the PHP Foundation – a non-profit that maintains and develops popular coding language – found a theoretical flaw in PHP but couldn’t figure out how a human hacker could actually use it in an attack.
In July 2026, the PHP Foundation got accepted into OpenAI’s Patch the Planet initiative, which is aimed at using frontier artificial intelligence (AI) to find flaws in popular software and fix them using AI.
In August, a cyber security firm called Calif – which was part of the project – found a serious flaw in PHP, which researchers at OpenAI and Wiz also found shortly after.
Since then, the foundation had been working with the companies on a software patch that could be downloaded by PHP users to fix the flaws, with a plan to release the fix in late October.
But a leak of the basic details was circulated ahead of time on social media, forcing the PHP Foundation to bring forward its announcement.
According to PHP, researchers at Calif then “mistakenly published a video” showing some basic details of how the flaws could be used to hack various websites.
The video was deleted but shared widely in hacking forums, leading to criminals trying to figure out how the hack works. Researchers say the criminals themselves are using AI to ‘vibe code’ a method of attack.
That’s why the patch has been rushed out and sites have had to be taken down in case attackers use the flaws to carry out cyber attacks.