
The device could allow unauthorized individuals to remotely unlock doors, disable the ignition, and even honk the horn while drivers are on the road.
SAN DIEGO — Researchers at UC San Diego are warning car owners about a dealer-installed anti-theft device that may put millions of vehicles at risk. The device, found in over 2.2 million cars, many of which they say were sold in Southern California, was designed to help prevent theft from dealerships but has been identified as a potential security vulnerability.

This story continues below.
Aaron Schulman, a professor at UC San Diego, explained that the device could allow unauthorized individuals to remotely unlock doors, disable the ignition, and even honk the horn while drivers are on the road.
“In our research, we discovered that [the] system is vulnerable to anyone connecting to any of those 2.2 million cars and unlocking the doors, disabling the ignition and even causing you to have your horn honked while you’re driving down the highway,” Schulman said.
The vulnerability could be one of the largest vehicle security issues ever identified, according to researchers. According to Schulman, the situation is particularly concerning in San Diego, which is the epicenter of sales for these vehicles.
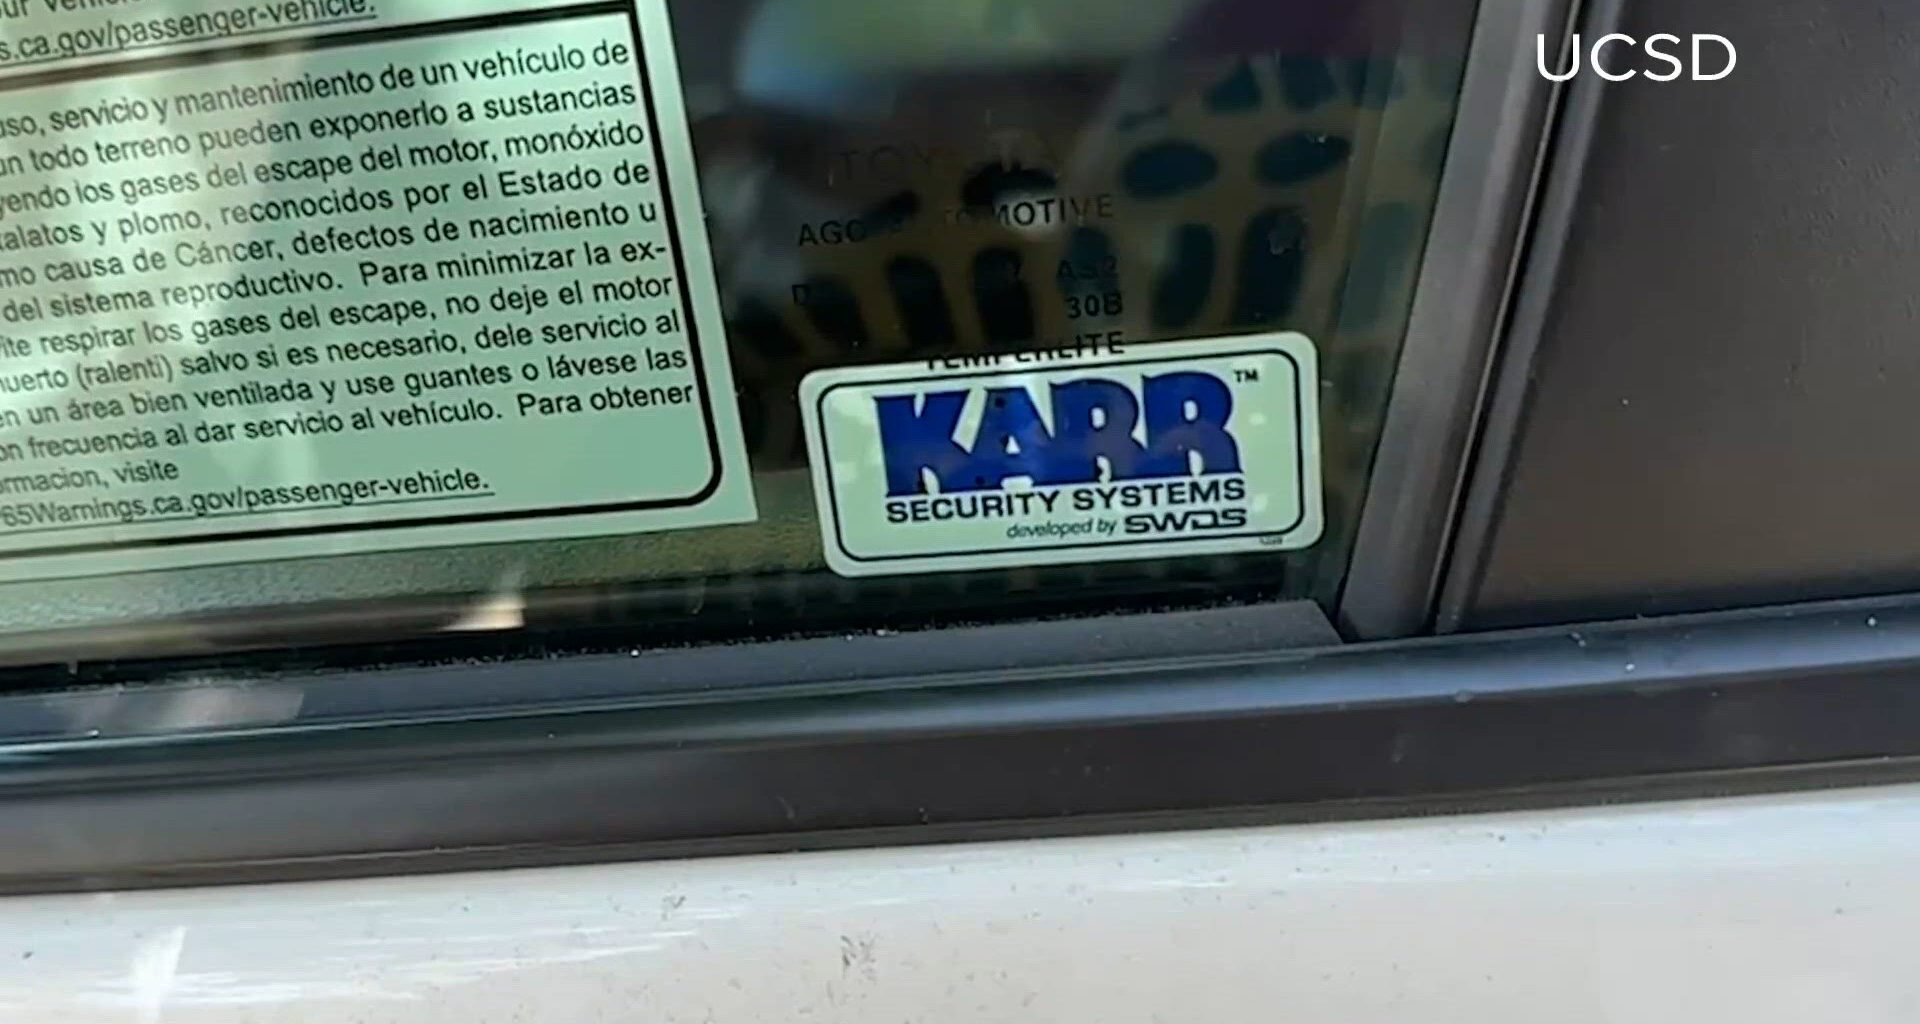
To check if a car has the anti-theft device, owners are advised to look for a sticker on the driver’s side window indicating its presence. However, if a vehicle does not have the sticker, it may still have the device installed.
“If you’re one of these people who have bought any vendor of car, whether it be Honda, Toyota, Ford, you name it, you need to check on your driver’s side window if you see the sticker that says KARR, you may have this system,” Schulman said.
Schulman said drivers will have to manually update their vehicle; he emphasized there is no automatic update
A KARR Security spokesperson said it was mentioned in the UC San Diego research as one example among many companies using Bluetooth-enabled anti-theft device technology and said this is not just a KARR Security issue. They also mentioned there are no confirmed reports of this vulnerability being used against a real customer.
KARR Security provided News 8 with the following statement:
“KARR Security maintains rigorous standards to help protect customers’ vehicles. Researchers at UC San Diego identified a vulnerability affecting BLE-based auto theft devices, including a small percentage of KARR devices with certain Bluetooth-related components. The vulnerability described in the research is highly complex and presents a low risk to customers under real-world conditions. Nevertheless, we responded promptly and developed a firmware update to address the issue. We launched this app/firmware update on July 20, 2026. Active customers may apply the update directly from their phone after securely logging in to the KARR Security app. Vehicle owners of non-active systems can still update via the app using their VIN (last 8 digits) as a validation step. Consumers can find detailed instructions and tutorials for assistance with this firmware on the Customer FAQ section of our website at www.KARRSecurity.com.”