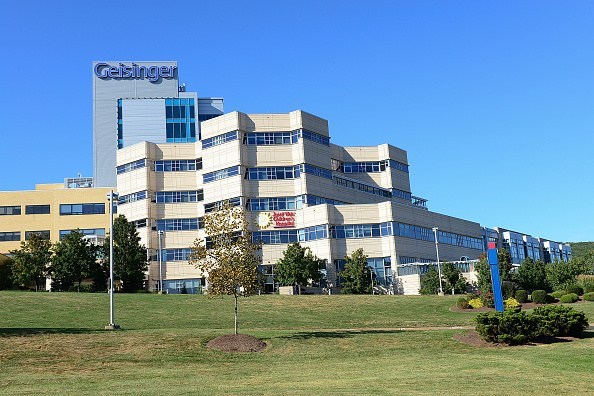
The Geisinger health system based in Danville announced Monday it is notifying fewer than 2,000 patients that some of their personal information may have been compromised in a recent data breach involving the hacking of an employee’s email account.
Geisinger offers free identity protection to the potentially affected individuals of the Aug. 20 “data security incident,” according to the announcement. It did not identify the employee or that person’s position or location.
Details released include:
• On Aug. 20, Geisinger discovered suspicious activity involving an employee’s email account. Upon identifying the issue, Geisinger immediately secured the account, launched an investigation with the assistance of cybersecurity professionals and implemented measures to help prevent further unauthorized access.
• The investigation determined an unauthorized third party gained access to an employee’s email account. A subsequent review found the account contained information related to certain patients.
• The information involved may have included patient names, medical record numbers, dates of birth, dates of admission, event or service, and health insurance carrier names. Geisinger found no evidence that claims or insurance identification numbers, credit card or bank account information, Social Security numbers, or other sensitive medical information were accessed or acquired as part of this isolated incident.
“Protecting the privacy and security of our patients’ information is a responsibility we take very seriously,” said Jonathan Friesen, associate chief legal officer for privacy and innovation at Geisinger. “We are committed to maintaining our patients’ trust and have taken steps to secure our systems, investigate the incident, and further strengthen our safeguards to help prevent a similar incident from happening in the future.”
Although Geisinger is not aware of any misuse of patient information related to this incident, it is offering potentially affected individuals complimentary enrollment in Experian IdentityWorks, a comprehensive identity protection and monitoring service, for a period of two years.
Data breaches hit health care sector
It was the latest data breach in recent years targeting regional healthcare providers and an insurance company or their contractors.
Two data breaches in 2023 led to class-action lawsuits that resulted in multimillion-dollar settlements, including:
• In March, a federal judge approved a $5 million settlement in a class-action lawsuit brought over a widespread data breach in 2023 that compromised the personal information of about 1.3 million Geisinger patients. In that incident, Geisinger announced in June 2024 a data breach involving an outside contractor discovered during November 2023 had left information for over 1 million patients vulnerable.
• In 2024, Lehigh Valley Health Network reached a $65 million settlement in a class-action lawsuit over data breaches of medical records of 134,000 patients. The lawsuit stemmed from a cyberattack by the Russian ransomware group BlackCat that targeted Lackawanna County-based Delta Medix Group, part of LVHN’s network. The data breach exposed patients’ personal information to the dark web. LVHN reported in February 2023 that hackers posted sensitive photos and information on the dark web after the organization refused to pay the ransom the hackers demanded. While there had been larger class-action lawsuit settlements in terms of total dollars and numbers of plaintiffs in cases throughout the country, the LVHN pact might have been the largest class-action settlement per-capita in the nation, the plaintffs’ attorney had said.
Meanwhile, another data breach in 2023 involved Commonwealth Health System. In July of that year, Commonwealth Health announced hackers breached a Scranton cardiology group’s computer network and potentially obtained the private data of 181,764 patients and others. The breach of the cardiology group occurred Feb. 2 in data maintained by Commonwealth Health Physician Network-Cardiology, also known as Great Valley Cardiology (GVC), and wasn’t discovered until April 13. Commonwealth Health said the group learned of the incursion from the U.S. Department of Homeland Security, which tracks potential cyber threats. The cardiology group disconnected its network from the internet, disabled VPN access to prevent further access and referred the matter to law enforcement. Information exposed, which was not thought to have been used by hackers, varied from person to person and included names, addresses and demographic information such as dates of birth; Social Security, driver’s license and passport numbers; credit card or debit card and bank accounts; and health insurance, claims and medical information of dates of service, diagnoses, medications and lab results.
Other prior incidents
According to archives of The Times-Tribune and The Citizens’ Voice, other data breach incidents going back to 2020 have included:
• A business associate of both Wilkes-Barre General Hospital and Moses Taylor Hospital in Scranton had paper and films compromised when a tornado struck its medical records storage facility April 27, 2020, affecting 518 Wilkes-Barre General patient records and 1,905 Moses Talor patient records.
• Geisinger Wyoming Valley Medical Center in Plains Twp. had electronic medical records breached on May 8, 2020, affecting 805 individuals.
• A Lehigh Valley Health Network business associate’s network server was hacked with ransomware on Sept. 14, 2020, affecting 81,487 individuals.
• Geisinger Health had electronic medical records breached on Sept. 23, 2020, affecting 717 individuals.
• A Geisinger business associate’s network server was hacked with ransomware on Oct. 19, 2020, affecting 86,412 individuals.
• Geisinger Health Plan had unauthorized access to paper/films on Feb. 28, 2021, affecting 2,872 individuals.
• A Highmark subcontractor’s network server was hacked on March 11, 2022, affecting 67,147 individuals.
• A Highmark business associate’s network server was hacked on June 30, 2022, affecting 511 individuals.
• A Lehigh Valley Women’s Medical Specialties business associate’s network server was hacked with ransomware on Nov. 30, 2022, affecting 4,535 individuals.
• A Highmark employee fell victim to an email phishing scheme on Feb. 10, 2023, that affected 239,039 individuals.
Steve Mocarsky, staff writer for The Citizens’ Voice, contributed to this report.